Groundhog day 
It’s like the old folks home where everyone knows everyone else’s joke. So they just yell out… number 46 (or some other number) and everyone rolls around laughing.
Groundhog day
It’s like the old folks home where everyone knows everyone else’s joke. So they just yell out… number 46 (or some other number) and everyone rolls around laughing.
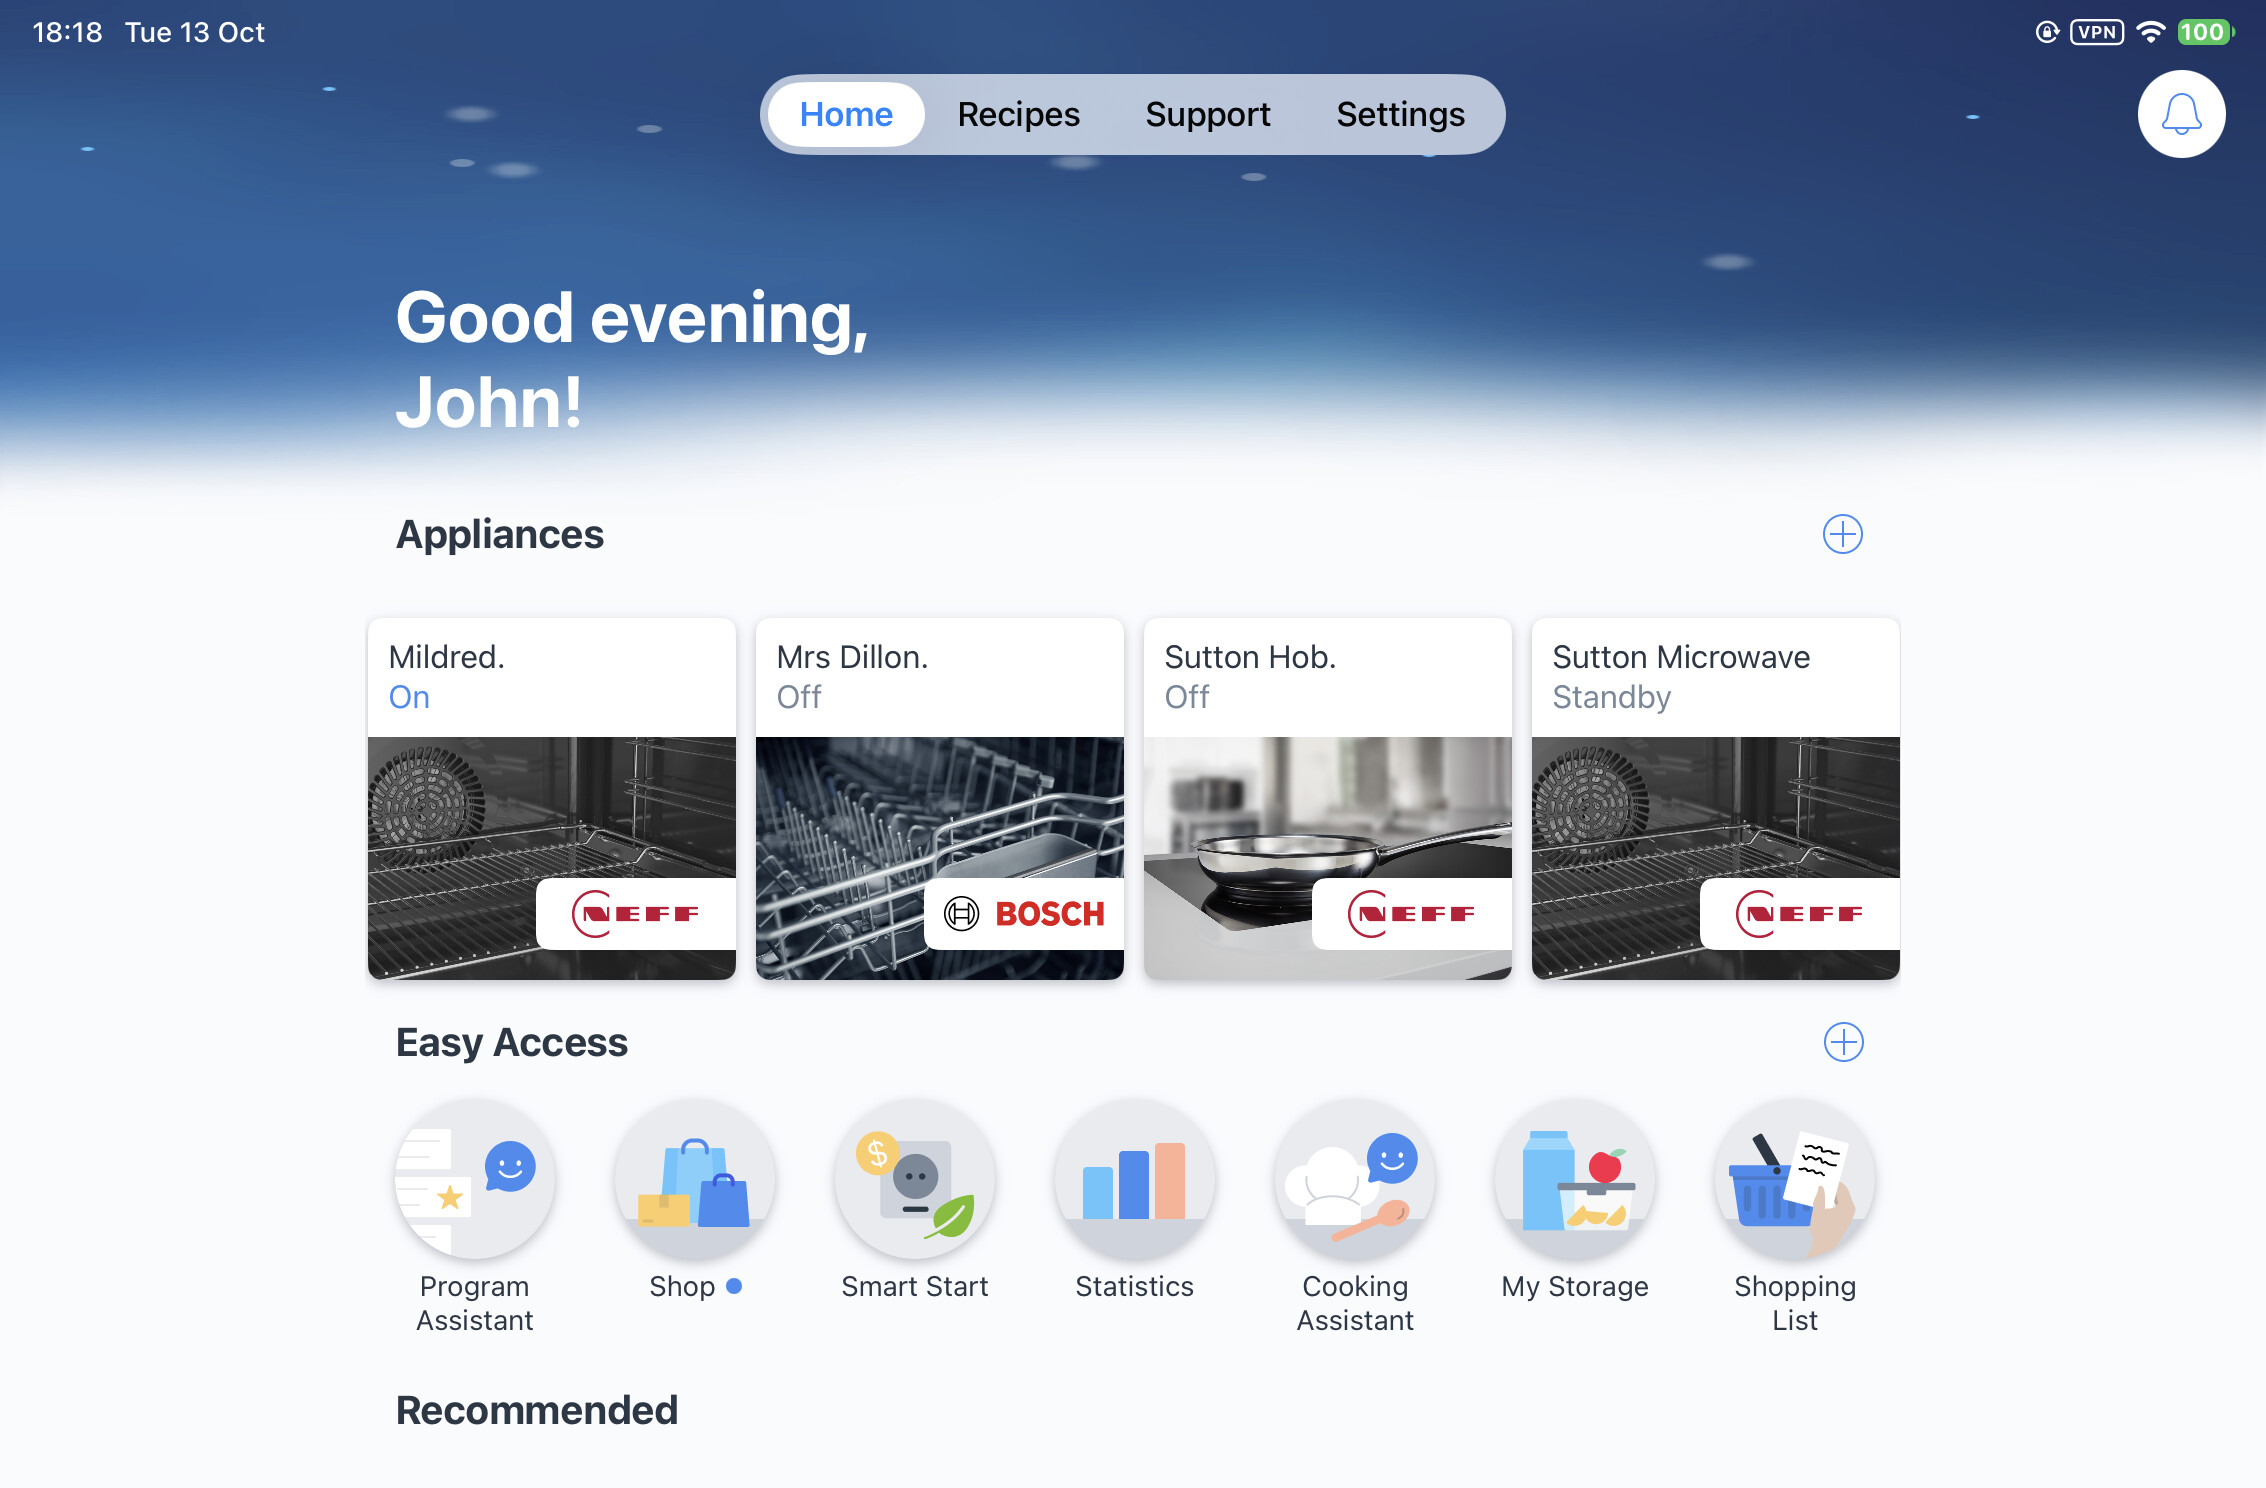
Most of our kitchen appliances are now connected to the net, all excluding washing machines and fridges (though they have connected temp alarms) I think. There’s little point really but if they can be, why not. The only worry is you might accidentally turn on oven 2,000km away.
One location…
Mildred is a double oven and Mrs. Dillion is a dishwasher. I might call the hob in that location Elon, because it controls the extractor and maybe the microwave Little Marco.
Because there’s little point and they all increase the attack surface?
We use Mr. Propre to attack our surfaces.
But more seriously, I don’t think a hack into the Home Connect servers would lead them through my appliances into my home wifi and into our phones, iPads, laptops or iMac. There’s firewalls, a VPN and along the way plus our devices own protection. Companies just don’t think security is worth investing in. Better to spend the money on some crappy app that lets’s you know there’s a special on steamed chicken feet this week
I don’t think hackers (and I know that’s an abuse of the term) are generally clever, I think they are lucky. Bad security is at the heart of it.
“Danfoss said the affected cold units were older models whose security software could not be updated to ward off a risk they had identified.
The firm added in a statement that it had “long advised” businesses to keep supported systems up to date.”.
Was the problem with these fridges not that the username to access them was admin, and the password was a daily changing one (good security) that just changed each day to the current date?! (Terrible security). I’ve read that several times now. If they’re unable to patch these older machines then it was just a ticking time bomb really.
The second statement is incompatible with the first.
If systems were vulnerable, could not be updated and were left on the internet then someone goofed at some point in that chain.
That is true enough - many are just “script kiddies” who can download and run an exploit without understanding it - but…
Mmm - as I said you can look at any connected system and see streams of probes looking for open ports and known vulnerabilities. I get, as I said, about one every two seconds on my remote servers - 43,200 probes a day, seven days a week, 52 weeks a year. That will find the holes in your network eventually.
Yes.
I need to look at mine. I only really need 2 ports open, SSH and my IPTV proxy.
Worthwhile moving ssh to a non standard port if you can 2222 is common and cuts down on door knockers quite a bit.
I think the first statement referred to the obsolete equipment, the second was just standard advice, like any S/W provider would advise.
That’s a lot of probes. I suppose, as they say, the harder you try the luckier you get.
I think, like scam mail, there needs to be a more concerted effort at a country, regional and indeed global level at tracking down sources. I don’t have the answer, and VPNs make tracking even more complex, but countries that are hosting scammers and hackers do need to be sanctioned. Or flipping that, maybe a new “safe” designation could be a way forward, and everything else is flagged.
That’s the thing though - when a vendor says “of course you must keep all hardware up to date with current firmware for continued security protection” and “oh, but that system is too old to be updated” it starts to sound like blackmail and I get the irresistible urge to visit their closest data centre and give their servers an immediate reprogramming with a large axe.
All business’s should carry out a business vulnerability case. Still many of these cyber attacks might calm down a bit no that the Ukraine have bombed Putin’s data centres 
Looks like our Mildred and her siblings could be exposed  I wondered why Neff fitted her with a Nvidia GB300 NVL72
 If they ever get our microwaves cranked up we’re in real trouble

Probably millions of home routers are infected with malware which is hooked up to control and command stuff - ideal for botnets, renting out CPU cycles, hiding your traces, and general havoc as well as a route into networks as the router is seen as “trusted”.
Security is often seen as a relatively low priority in embedded systems and firmware never gets updated.
Which is why I run Linux on my switches and routers and try to keep things up to date.
It’s an irritant that Sosh/Orange don’t allow you to use your own modem/router.
Google’s currently trying that. Sending messages and popups rhat say " you must update your o/s otherwise we are not guaranteeing that Google apps will continue to work and they may stop". My o/s is not that out of date but it’s out of Samsung’s apparent commitment to update - phone manufacturers windows to provide updates are unrealistically short but it is what it is.
Just makes me think perhaps getting out from under US tech domination, given the way that country is going, to something open source and preferably not US controlled may become more urgent than thought
Quite.
I’m not sure it’s encouraged on SFR/RED but I know there is at least one fairly lengthy thread on one internet forum (not this one) where people have used their own kit. It’s mostly (possibly entirely) people who have an ONT which presents the raw connection as Ethernet - not one which is just an optical terminal and the router takes fibre from that and provides the ONT functionality internally, which is what I have.
However there are optical transceivers which have been modified and apparently do work to give the full 2.5G connection on a single interface. I bought one but have not had chance to play. It does not help security too much except that they are “different” to the standard kit - they run custom versions of OpenWrt which (in contravention of the GPL) don’t tend to supply source or many updates.
Not that easy to get TV or phone services working either.
I couldn’t agree more, but also banking and other areas that haven’t occurred to me yet. The bloody dunderheads leading the EU can’t see the risks, they have to be dragged inch by inch from the cosy past to the scary reality of today. How many times do they need to be “shocked”. Do they think that even after Trump is gone that things will return to the happy clappy times?
Trump is quite happy to see Ukraine loose the war if it helps him do better in the midterms.
Somebody (sorry, I forget who) posted a link to an excellent interview with Geoffrey Hinton which I watched. He obviously despises Trump, and rightly so. When discussing the risks of AI one of his comments stood out I thought, “if Trump had to make a decision between saving humanity and further enriching his family, which do you think he’d choose”. Pretty succinct and based on past performance we all know the answer. The interviewer, a good guy, seemed flummoxed by the question, as did the audience. But this is the President the World is dealing with. In my opinion there is nothing too bad that Trump won’t do now, let alone if cornered. Fingers crossed for the midterms, if they ever happen.
Here’s an article that references the interview I mention above. Well worth a read 
Something of the same here, I had to change a perfectly functioning IPhone only 4 years old for a new one and a Samsung tablet because of security updates on the OS are no longer compatible, happy to get rid of the Samsung android and have a M5 IPad Pro in its place. All this is money making for the company’s and recycling, what a waste…
Apple are generally quite good at making updates available for older hardware, Samsung promise support for the A56 out to Android 21.
Or you might be lucky and find your phone is supported by Lineage OS.
Company IT boffins say no longer compatible so we change, probably ok for Jo public but not for us or our clients.