Surely a NDA is agreeing not to say anything which would include the truth thus allowing others to decide someones fate without knowing all the facts.
Surely a NDA is a form of protecting a company from any wrongdoing which I have no doubt is the case with the post office and Horizon.
As an aside my wife, an ex civil servant, signed the official secrets act when commencing her employment many years ago which I presume is still the case today.
Is that a government version of an NDA?
The truth is hard to find, and sometimes impossible.
I think that the really big issue with Fujitsu staff being able to access postmasters accounts remotely is that there was no audit trail. This meant that there was no means of going back and finding out which account had been accessed remotely by who and what was done. All that could be seen is that something was done to the account, and it was assumed that it had been done by the postmaster.
Edit: It has been reported, and I think it was also in the TV program, that there was no audit trail for remote access, but I don’t know for sure that it’s true. If it is, then that’s a huge hole in the system that could have been exploited by a bad actor with access without leaving any evidence.
2 Likes
I told the truth to the board, with evidence, from then on its their decision. I took my advice from my solicitor. If the board cover it up then thats up to them. They did take action after I had left and another occurance of wrong doing happened. In this case it did not revolve around ruining people’s lives.
It’s a bit more nuanced than that, as was brought out in the TV series. Basically, they were repeatedly asked if the Post Office could remotely access accounts, and they repeatedly said no, which was actually true, as Post Office staff couldn’t. What they failed to mention is that Fujitsu could access accounts remotely, but that question was not asked until much later in one of the court cases.
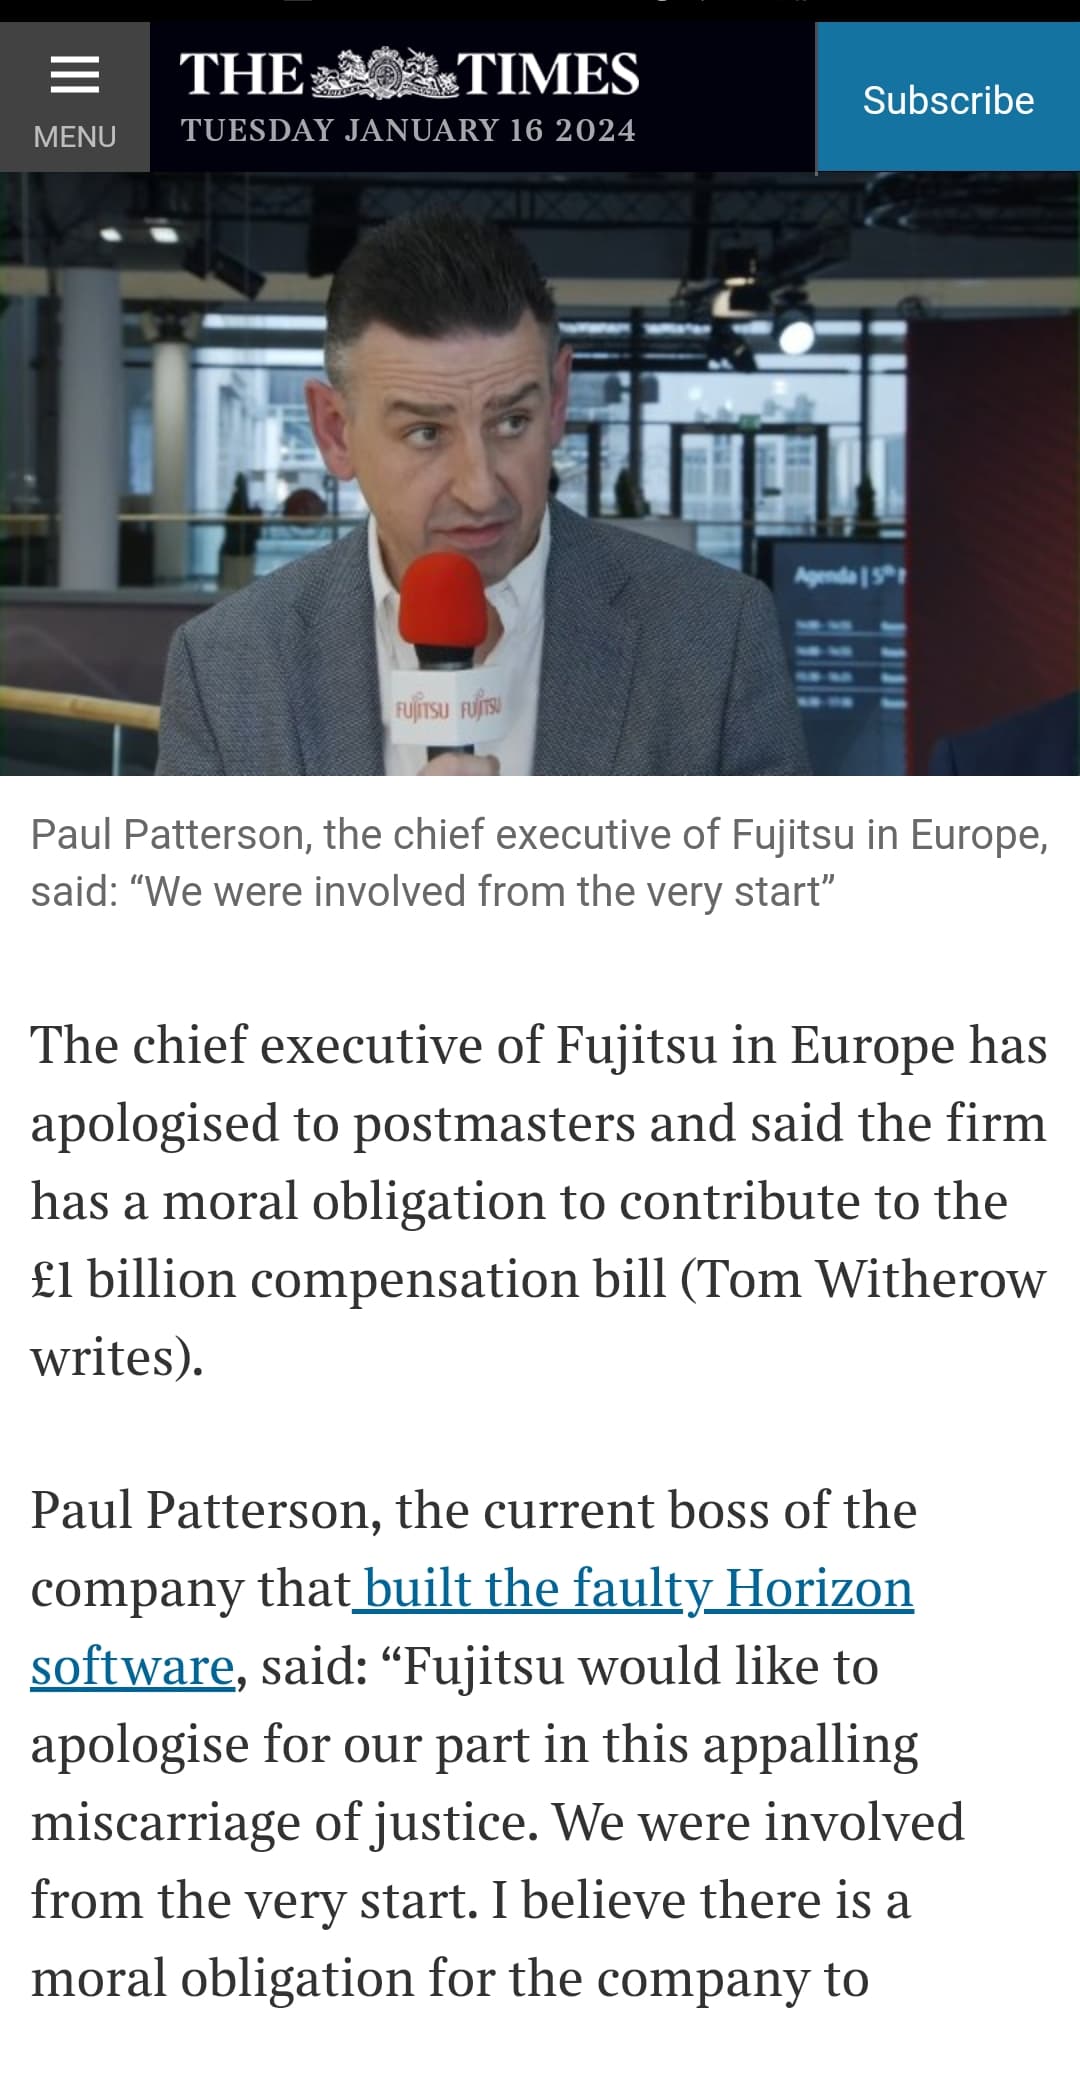
Just seen that the CEO of Fujitsu has admitted they were aware of issues and that they have a moral duty to contribute towards the compensation.
4 Likes
How refreshing.
1 Like
From that statement Geoffrey I deduce you a haven’t ever been within an ass’s roar of an IT project in your life. 
2 Likes
Just watching a Fujitsu employee giving evidence. It featured several software problem reports from way back, over ten years ago. The problem description fields state transactions going missing at EOD and duplicate records all over the place, The Post Office and Fujitsu (ICL) knew this was a crock (technical term🤭) since 2008/2010.
Senior heads should roll.
1 Like
Or jumping before being pushed.
I suspect Fujitsu’s lawyers’ interpretation of moral responsibility maybe different to ours (or indeed his). The execs responsibility is to minimise shareholder loss, regardless of morals🙄 So the “payout” will need to be justified. Loss of future business due to reputational damage? I dunno, but I wouldn’t like to be making the argument in Fujitsu HQ.
In larger towns there are Crown Post Offices owned and run directly by the Post Office (as opposed to sub-postmasters who ran their own business). These presumably also relied on Horizon software and showed the same shortfalls. Did the Post Office prosecute itself or did the shortfalls just disappear?
Good question. Maybe the accounting procedures are different? The person at the counter of the large post offices may be more akin to a checkout person than a sub postmaster, who’s really a little business with accounts to balance etc.
I wonder how they replaced all those ‘failed’ sub-postmasters, if they did, or did they close many of them altogether?
I can’t imagine anybody wanting to sign up to such an awful organisation.
Fujitsu in the news again… for all the wrong reasons! 
Fujitsu spilled private AWS keys, client data and plaintext passwords out into the open, unnoticed, for nearly a year according to a security researcher with the Dutch Institute for Vulnerability Disclosure.
Jelle Ursem told The Stack that the multinational had exposed a public Microsoft Azure storage bucket to anyone who encountered it (as he did) that was full of private data. The bucket, named “fjbackup” included:
- A full mailbox backup (thousands of emails) holding sensitive data.
- Extensive details on client activity and teams
- A CSV file of passwords pulled from password manager LastPass
- Scores of Microsoft OneNote files “with everything you need to know” about customers including Centrica and Dutch water utility PWN, which serves 1.7 million customers; among many others.
The cloud storage bucket sat exposed to the public internet from March 2022 to early 2023 before Ursem spotted it and disclosed it to Fujitsu.
1 Like
Not sure if this is related ?
1 Like
"[quote=“Gareth, post:94, topic:46367”]
[/quote]
" How do these people win critical government contracts again…"
The author must be quite young  It’s because twenty years ago they bought ICL who were in Government up to their incompetent eyes as they threw business at them to try and keep them afloat. I haven’t dealt with them in twelve years, but Fujitsu never have been, nor IMHO will ever be, a credible IT services company. Dross from the CEO down.
Words almost fail me, what a total lying bitch!
https://www.bbc.co.uk/news/live/uk-69042928
1 Like
Vile odious cretin. And she was, at the time, a high priestess of the church AND the recommended one by Welby to be bish of London 
2 Likes
Can’t bear to look at any photos of the horrible lying cow. If that had been here in France, she would be looking at doing porridge, over there, probably slap on the wrist and told not to do it again. The victims should go all out to sue her personally in a group action.
The victims haven’t got enough compensation to do that and she probably hasn’t hot enough personal wealth to make it worthwhile.